Microsoft GH-500 Exam Syllabus Topics:
| Topic | Details |
|---|
| Topic 1 | - Configure and use secret scanning: This domain targets DevOps Engineers and Security Analysts with the skills to configure and manage secret scanning. It includes understanding what secret scanning is and its push protection capability to prevent secret leaks. Candidates differentiate secret scanning availability in public versus private repositories, enable scanning in private repos, and learn how to respond appropriately to alerts. The domain covers alert generation criteria for secrets, user role-based alert visibility and notification, customizing default scanning behavior, assigning alert recipients beyond admins, excluding files from scans, and enabling custom secret scanning within repositories.
|
| Topic 2 | - Configure and use Dependabot and Dependency Review: Focused on Software Engineers and Vulnerability Management Specialists, this section describes tools for managing vulnerabilities in dependencies. Candidates learn about the dependency graph and how it is generated, the concept and format of the Software Bill of Materials (SBOM), definitions of dependency vulnerabilities, Dependabot alerts and security updates, and Dependency Review functionality. It covers how alerts are generated based on the dependency graph and GitHub Advisory Database, differences between Dependabot and Dependency Review, enabling and configuring these tools in private repositories and organizations, default alert settings, required permissions, creating Dependabot configuration files and rules to auto-dismiss alerts, setting up Dependency Review workflows including license checks and severity thresholds, configuring notifications, identifying vulnerabilities from alerts and pull requests, enabling security updates, and taking remediation actions including testing and merging pull requests.
|
| Topic 3 | - Describe GitHub Advanced Security best practices, results, and how to take corrective measures: This section evaluates skills of Security Managers and Development Team Leads in effectively handling GHAS results and applying best practices. It includes using Common Vulnerabilities and Exposures (CVE) and Common Weakness Enumeration (CWE) identifiers to describe alerts and suggest remediation, decision-making processes for closing or dismissing alerts including documentation and data-based decisions, understanding default CodeQL query suites, how CodeQL analyzes compiled versus interpreted languages, the roles and responsibilities of development and security teams in workflows, adjusting severity thresholds for code scanning pull request status checks, prioritizing secret scanning remediation with filters, enforcing CodeQL and Dependency Review workflows via repository rulesets, and configuring code scanning, secret scanning, and dependency analysis to detect and remediate vulnerabilities earlier in the development lifecycle, such as during pull requests or by enabling push protection.
|
| Topic 4 | - Configure and use Code Scanning with CodeQL: This domain measures skills of Application Security Analysts and DevSecOps Engineers in code scanning using both CodeQL and third-party tools. It covers enabling code scanning, the role of code scanning in the development lifecycle, differences between enabling CodeQL versus third-party analysis, implementing CodeQL in GitHub Actions workflows versus other CI tools, uploading SARIF results, configuring workflow frequency and triggering events, editing workflow templates for active repositories, viewing CodeQL scan results, troubleshooting workflow failures and customizing configurations, analyzing data flows through code, interpreting code scanning alerts with linked documentation, deciding when to dismiss alerts, understanding CodeQL limitations related to compilation and language support, and defining SARIF categories.
|
| Topic 5 | - Describe the GHAS security features and functionality: This section of the exam measures skills of Security Engineers and Software Developers and covers understanding the role of GitHub Advanced Security (GHAS) features within the overall security ecosystem. Candidates learn to differentiate security features available automatically for open source projects versus those unlocked when GHAS is paired with GitHub Enterprise Cloud (GHEC) or GitHub Enterprise Server (GHES). The domain includes knowledge of Security Overview dashboards, the distinctions between secret scanning and code scanning, and how secret scanning, code scanning, and Dependabot work together to secure the software development lifecycle. It also covers scenarios contrasting isolated security reviews with integrated security throughout the development lifecycle, how vulnerable dependencies are detected using manifests and vulnerability databases, appropriate responses to alerts, the risks of ignoring alerts, developer responsibilities for alerts, access management for viewing alerts, and the placement of Dependabot alerts in the development process.
|
Reference: https://learn.microsoft.com/en-us/credentials/certifications/resources/study-guides/GH-500
On the whole, the GH-500 guide torrent: GitHub Advanced Security recently can be classified into three types, namely dumps adopting excessive assignments tactics, dumps giving high priority to sales as well as dumps attaching great importance to the real benefits of customers. Our GH-500 dumps PDF files, fortunately, falls into the last type which put customers' interests in front of all other points. There are many advantages for our GH-500 torrent VCE materials, such as supportive for online and offline use for App version, automatic renewal sending to the customers and so forth.

Responsible staff
As far as I am concerned, the reason why our GH-500 guide torrent: GitHub Advanced Security enjoy a place in the international arena is that they outweigh others study materials in the same field a lot. Neither does the staff of GH-500 test dumps sacrifice customers' interests in pursuit of sales volume, nor do they refuse any appropriate demand of the customers. Aimed at helping the customers to successfully pass the exams, GitHub Advanced Security exam dump files think highly of customers' interests and attitude. Its staff put themselves into the customers' shoes so as to think what customers are thinking and do what customers are looking forward to. All in all, they have lived up to the customers' expectations (GitHub Advanced Security Dumps VCE).
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Supportive for online and offline use for App version
So long as you make a purchase for our GH-500 guide torrent: GitHub Advanced Security and choose to download the App version, you can enjoy the advantages of App version with complacency for you actually only need to download the App online for the first time and then you can have free access to our GH-500 test dumps in the offline condition if don't clear cache. Just imagine what large amount of network traffic this kind of App of our GH-500 exam dumps has saved for you. As you know, the network traffic is so highly priced that even a small amount will cost so much. Therefore, GitHub Advanced Security Dumps VCE files save a large proportion of money as it is a really economical decision. In addition, as our exam dump files are supportive for online and offline environment, you can look through the GH-500 torrent VCE and do exercises whenever you are unoccupied without concerning about inconvenience, which to a large extent save manpower, material resources and financial capacity.
Renewal in a year for free
As long as you have made a purchase for our GH-500 guide torrent: GitHub Advanced Security, you will be given the privilege to enjoy the free renewal in one year for sake of your interests. If there is any renewal about GH-500 dumps PDF materials, the customers will receive it in the mail boxes as we will send it to them automatically. In this way, you can renewal of the test information of GitHub Advanced Security Dumps VCE materials as soon as possible, which will be sure to be an overwhelming advantage for you. There is still one more thing to add up to it. In order to express our gratitude for those who buy our Microsoft GH-500 torrent files, we offer some discounts for you accompanied by the renewal after a year.


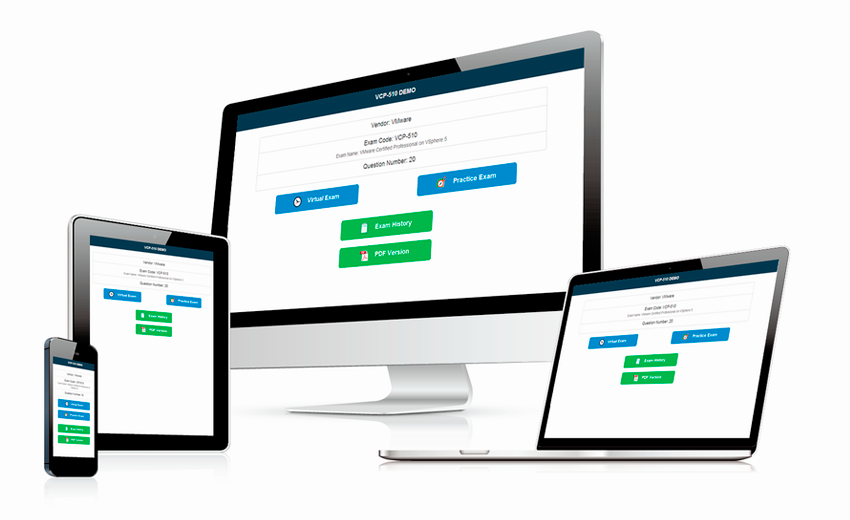
 Free Demo


 Bruno

 Maxine

 Susan
 Michell

 Lynn
 Dennis
 Zora
 Leif
 Abbott
 Moore
 Cleveland
 Kim
 Dennis
 Wythe
 Cash
 Gustave
 Harriet
 Ogden
 Zona
 Michaelia